The Evolving Battlefield of Network Security
Network-based intrusion detection systems (NIDS) monitor traffic to identify malicious activity. Signature-based systems identify known threats through pattern matching but struggle against advanced or unknown attacks. AI-based systems, leveraging machine learning and deep learning, excel at pattern recognition, yet remain vulnerable to adversarial machine learning attacks.
Adversarial Machine Learning: A Strong Opponent
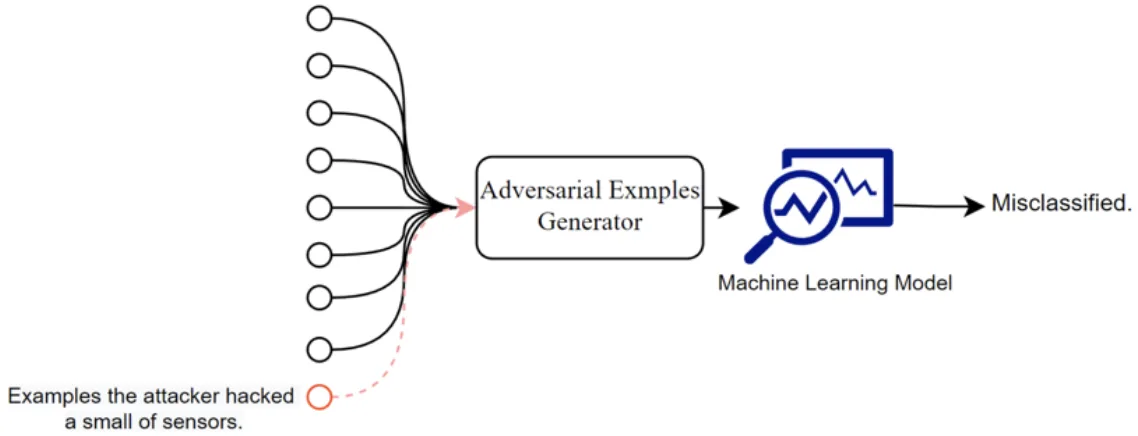
Adversarial machine learning studies how models interact with deceptive inputs designed to trigger errors. Attackers deliberately alter input data to deceive models, from changing pixels so autonomous vehicles misread traffic signs, to injecting modified packets to evade intrusion detection. The field is a necessary evolution in security, requiring continuous innovation to counter emerging threats.
These methods matter because AI increasingly protects mission-critical systems: fraud detection, spam filtering, network intrusion detection. As defences advance, attackers enhance their tactics in step. In regulated industries like finance and healthcare, regulators increasingly expect ML models to be resilient against adversarial attacks, and failures translate into financial and reputational damage.
Inside GANs (Generative Adversarial Networks)
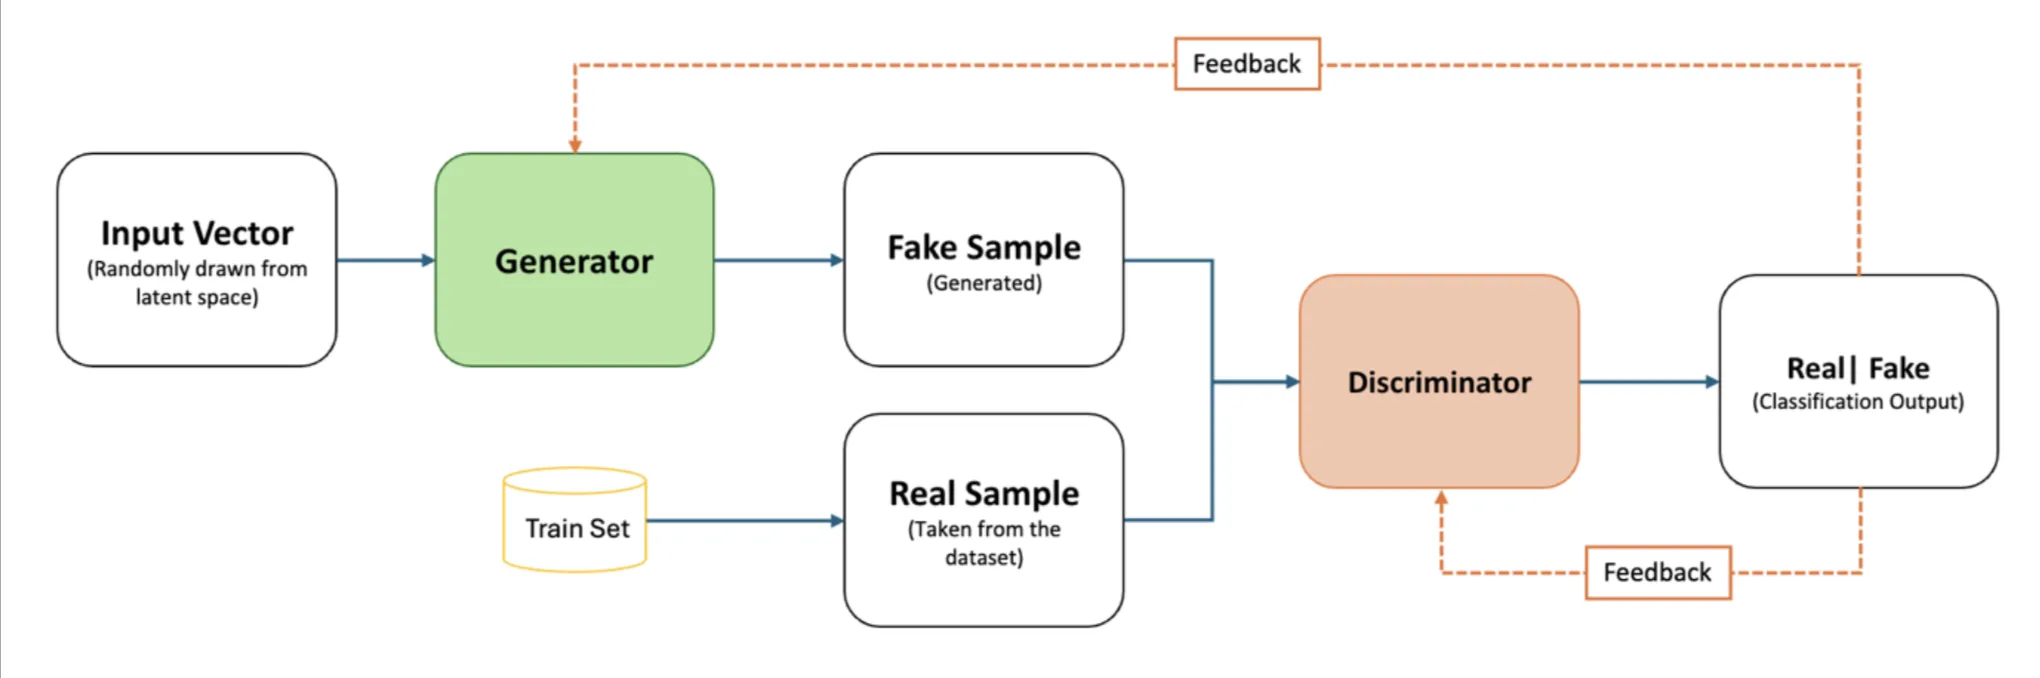
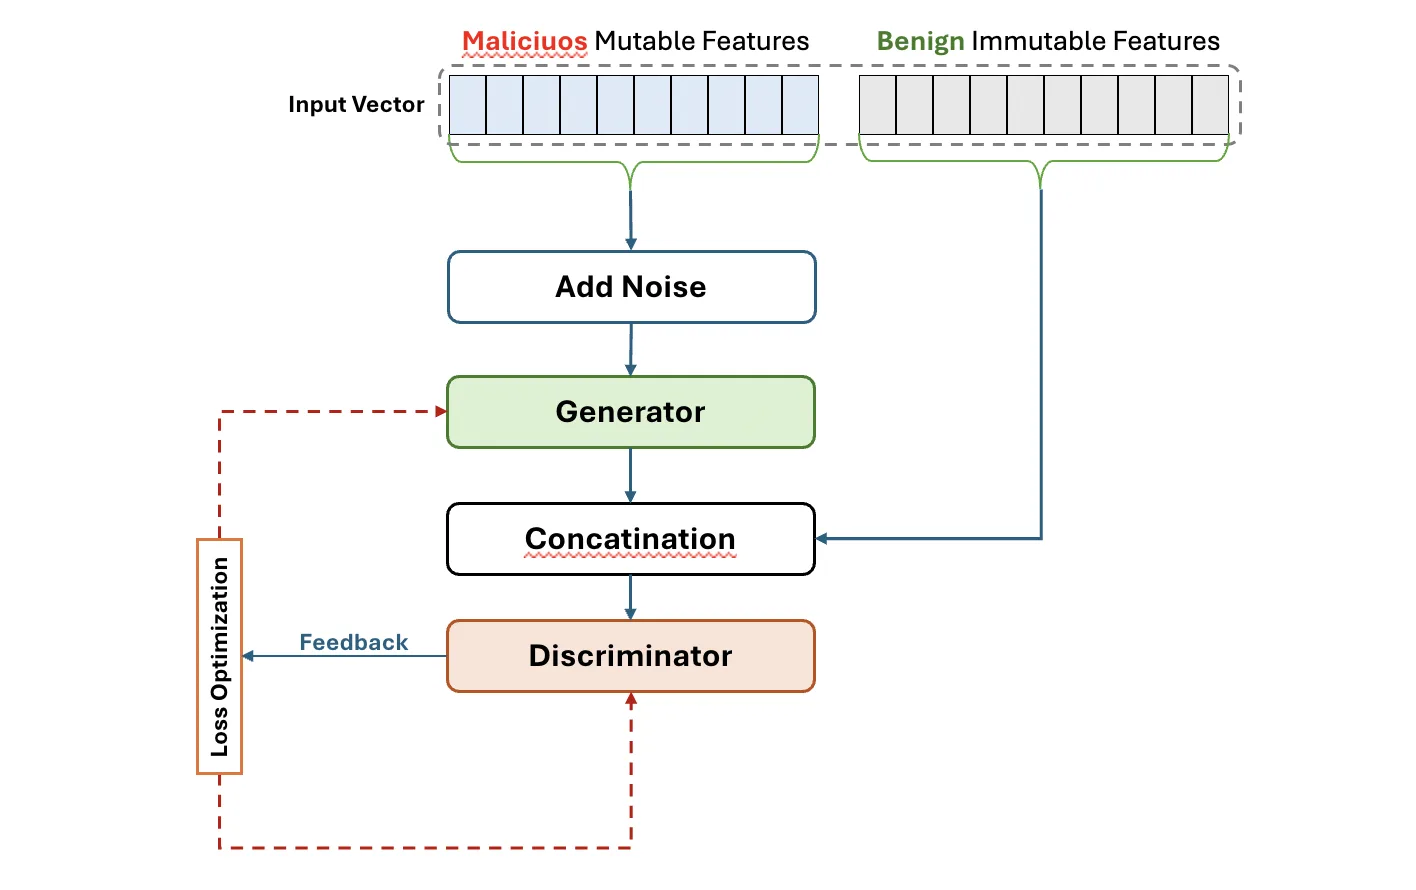
A GAN comprises two adversarial neural networks in continuous competition. The Generator creates data indistinguishable from the real world, beginning with random noise and transforming it to mimic genuine data, its objective is to deceive the Discriminator. The Discriminator acts as judge, evaluating both real and generated data to determine authenticity. Both improve iteratively until the Generator produces data so realistic the Discriminator can no longer reliably distinguish it, reaching a Nash equilibrium.
Testing NIDS with the NSL-KDD Dataset
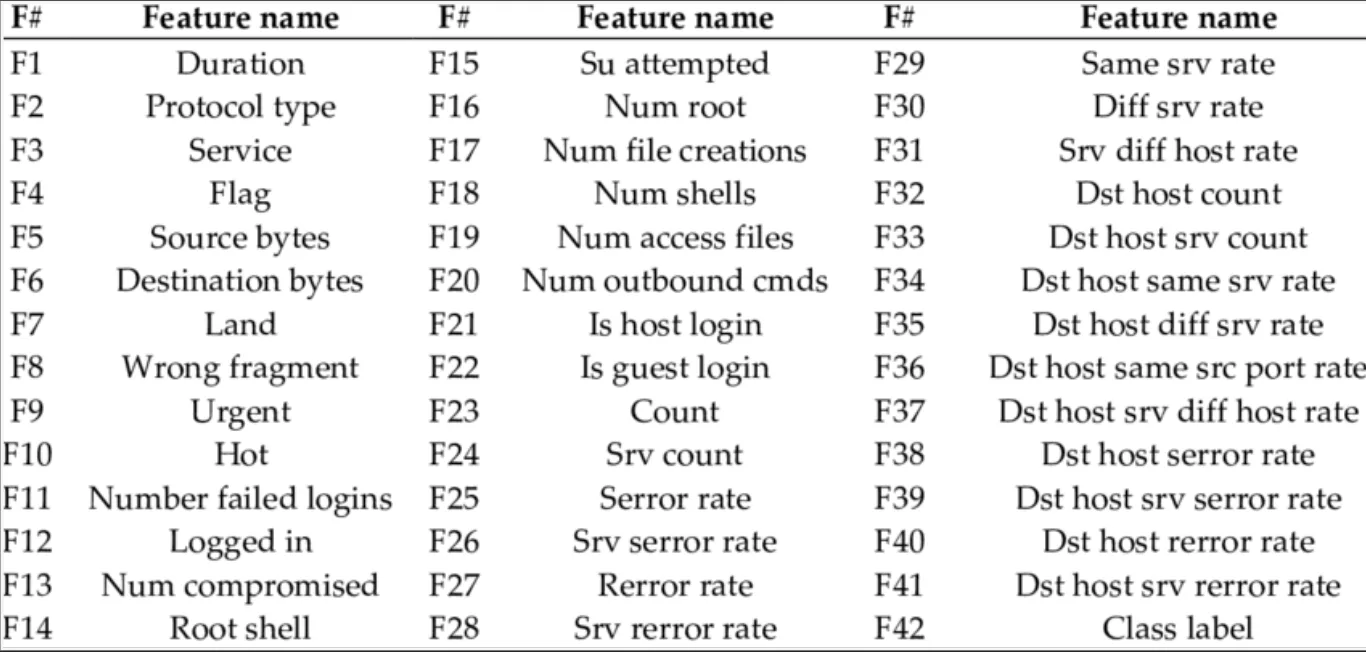
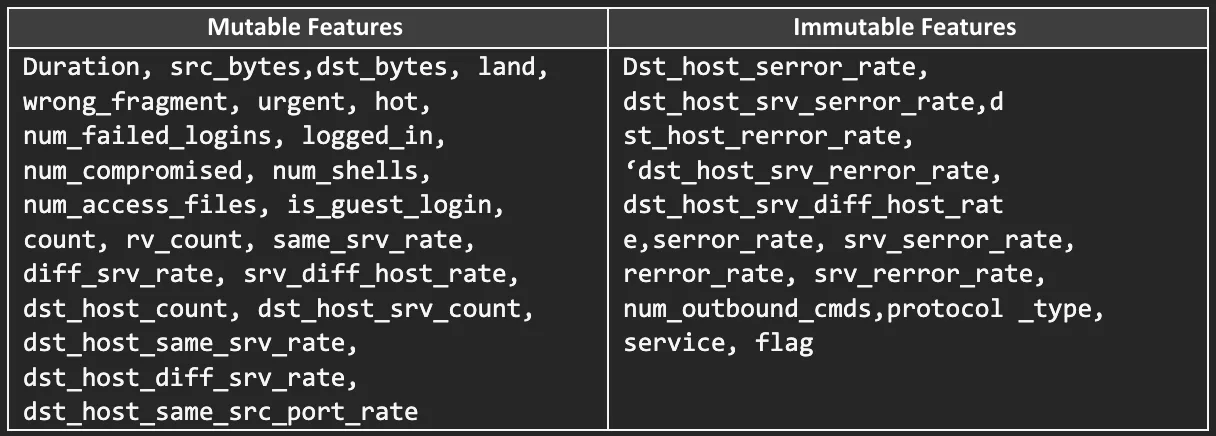
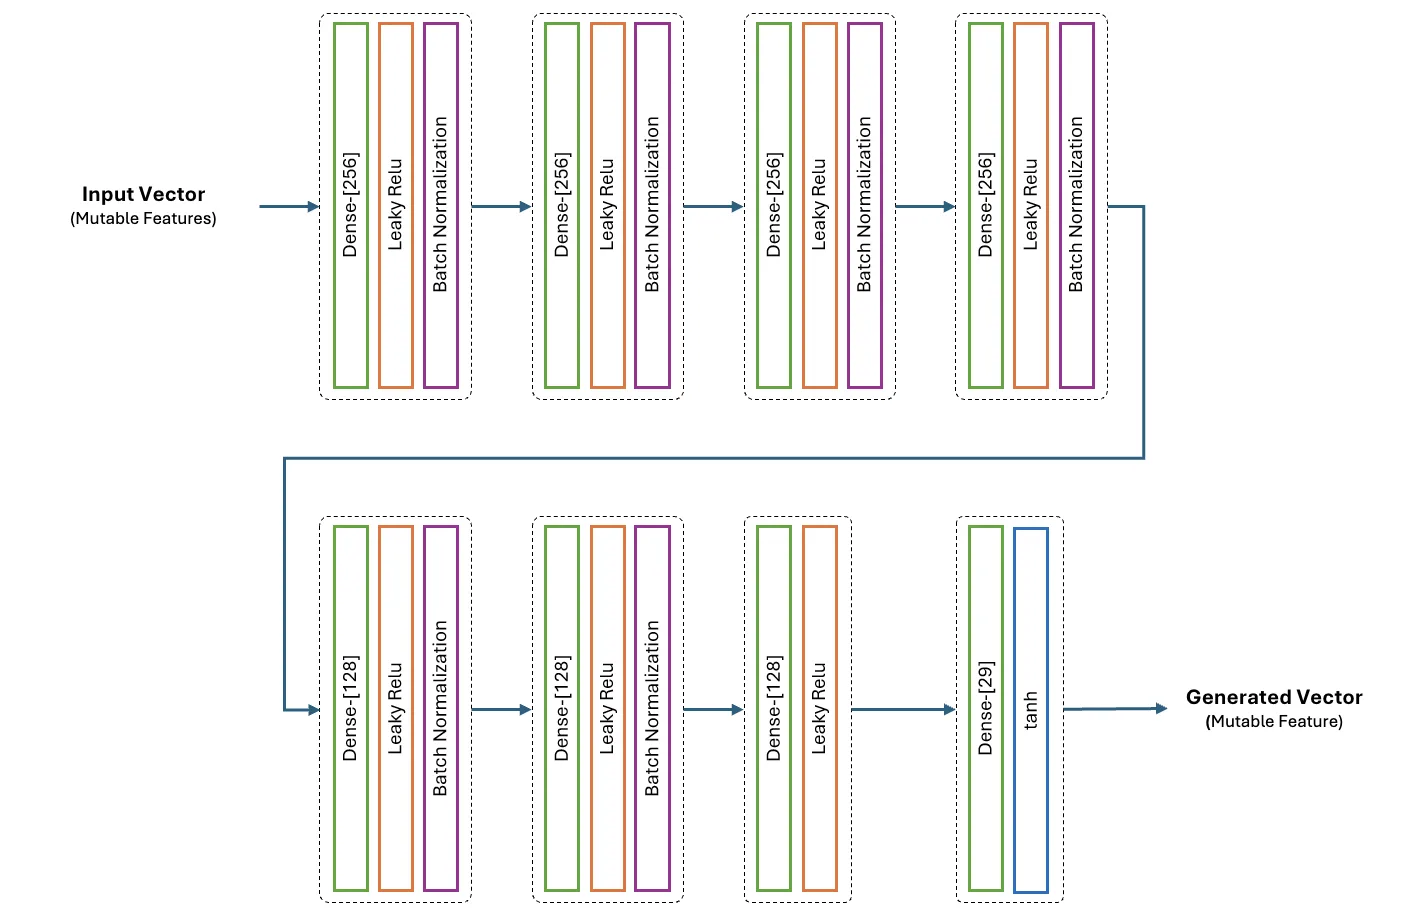
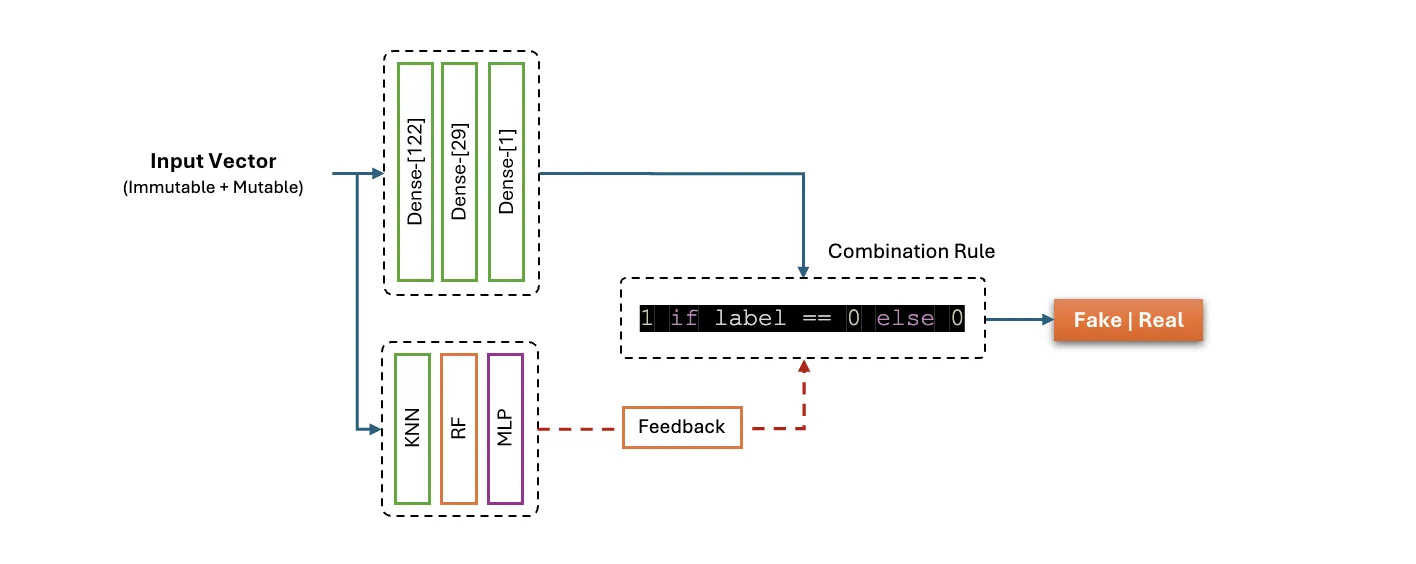
The NSL-KDD dataset, a refined version of KDD'99, is a premier resource for intrusion-detection research, with 125,973 training and 22,544 test records across 41 attributes per connection. We designed a GAN where the Generator produces synthetic traffic from random noise through dense layers (256→128 neurons, LeakyReLU, batch normalization, tanh output), while the Discriminator, enhanced by an ensemble voting classifier (KNN, Random Forest, MLP), distinguishes genuine from fabricated traffic.
Results
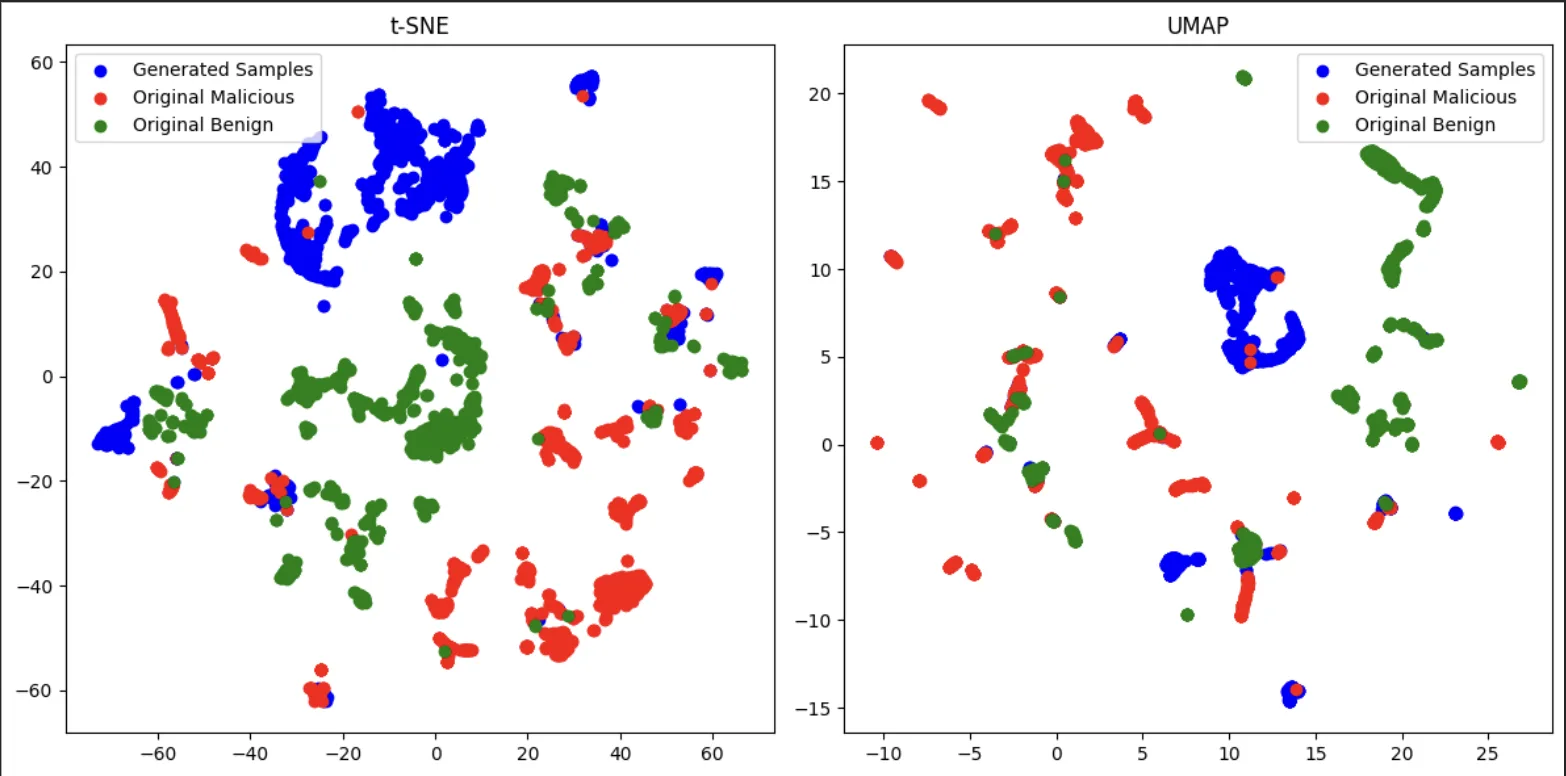
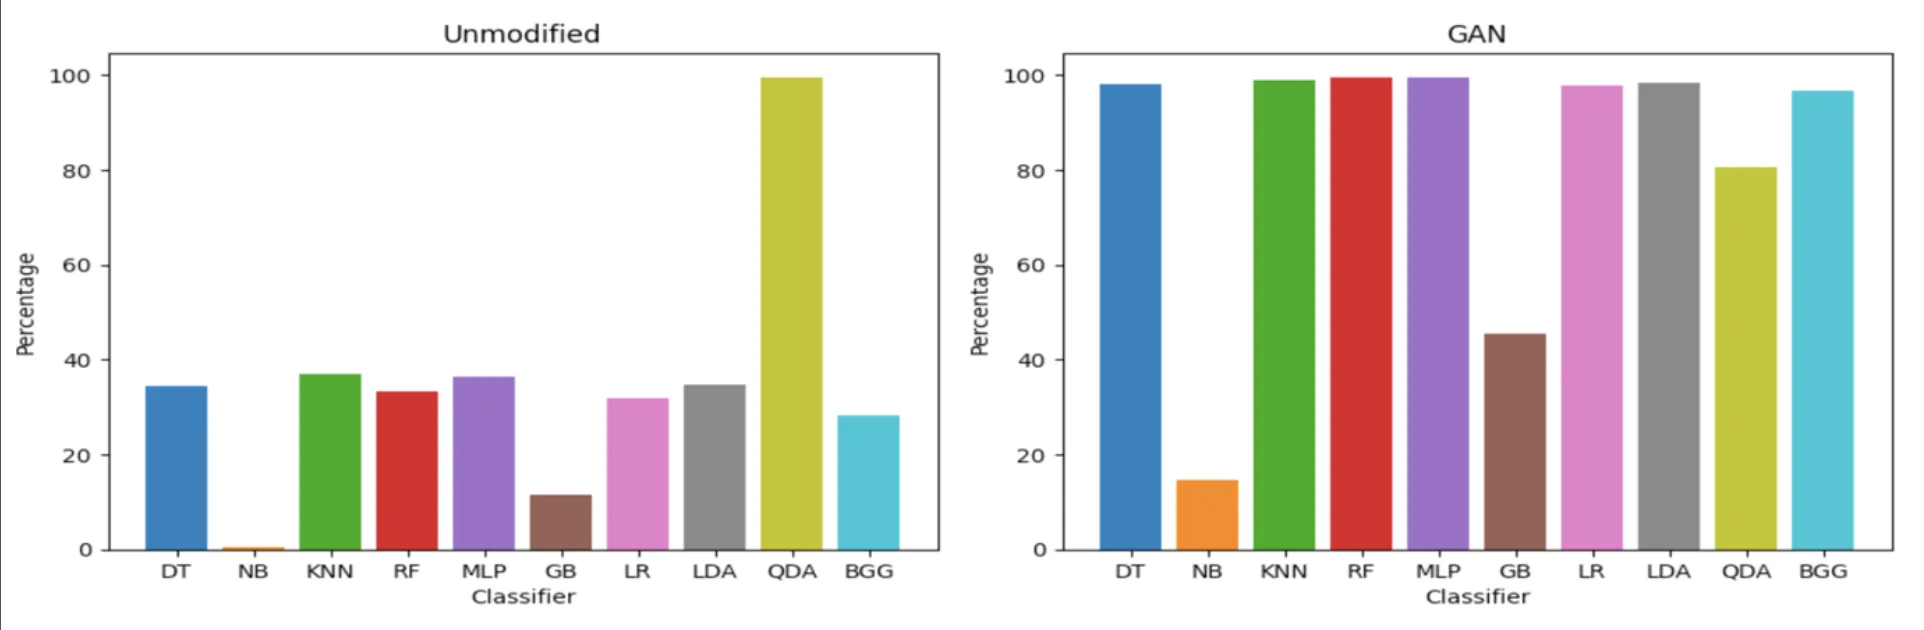
Classifiers vary widely in resilience. When exposed to generated adversarial examples, Naive Bayes showed low misclassification rates, indicating robustness, whereas K-Nearest Neighbor, Decision Tree, Random Forest, Multi-Layer Perceptron, Bagging, Linear Discriminant Analysis and Logistic Regression proved extremely vulnerable, misidentifying most adversarial examples as non-threatening. Dimensionality-reduction plots (t-SNE, UMAP) showed significant overlap between malicious, benign and adversarial samples.
Conclusion
The effectiveness of a NIDS depends largely on whether its ML models withstand adversarial attacks. GANs effectively highlight vulnerabilities in traditional detection by manipulating inputs to bypass defences. To stay ahead, teams must keep exploring defensive solutions and continuously train on emerging adversarial patterns to maintain resilience against evolving threats.